

LLM Security: Prompt Injection, Data Leakage and Safe Agents
A practical guide to LLM security: prompt injection, data leakage, agent tool use, RAG permissions, supply chain risk, red teaming and the controls that hold up in production.
Field notes from the founders and engineers at Sunday Labs on AI strategy, data platforms, agents and shipping to production.
A practical guide to LLM security: prompt injection, data leakage, agent tool use, RAG permissions, supply chain risk, red teaming and the controls that hold up in production.
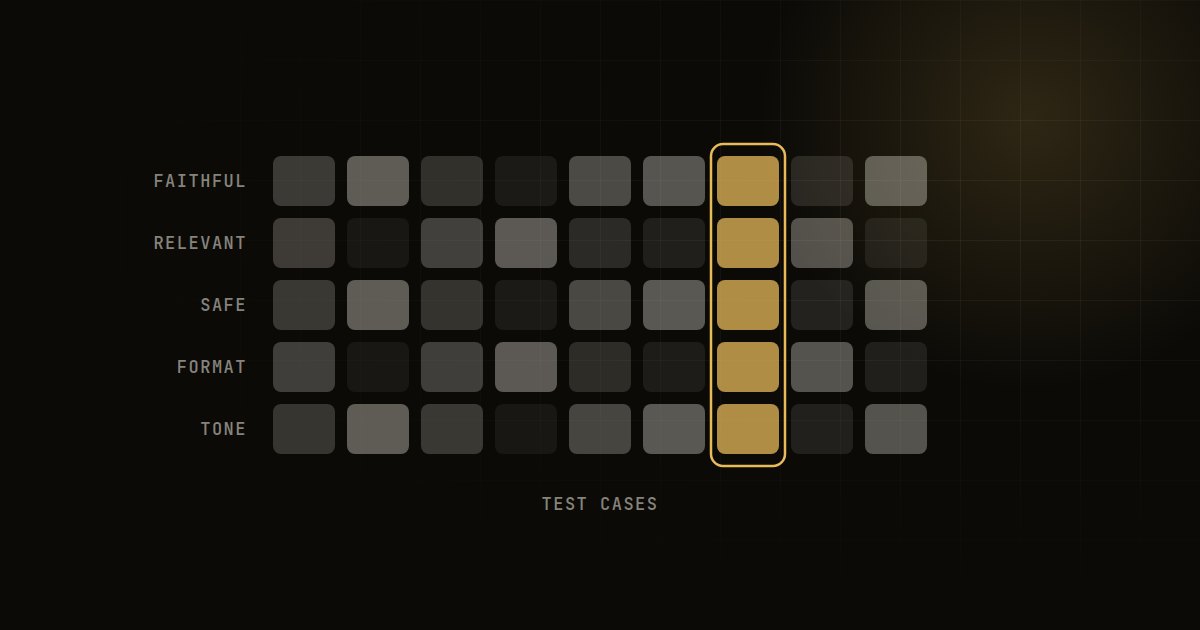
How to evaluate LLM applications properly: golden datasets, metrics that matter, LLM-as-judge done safely, regression testing and production monitoring.
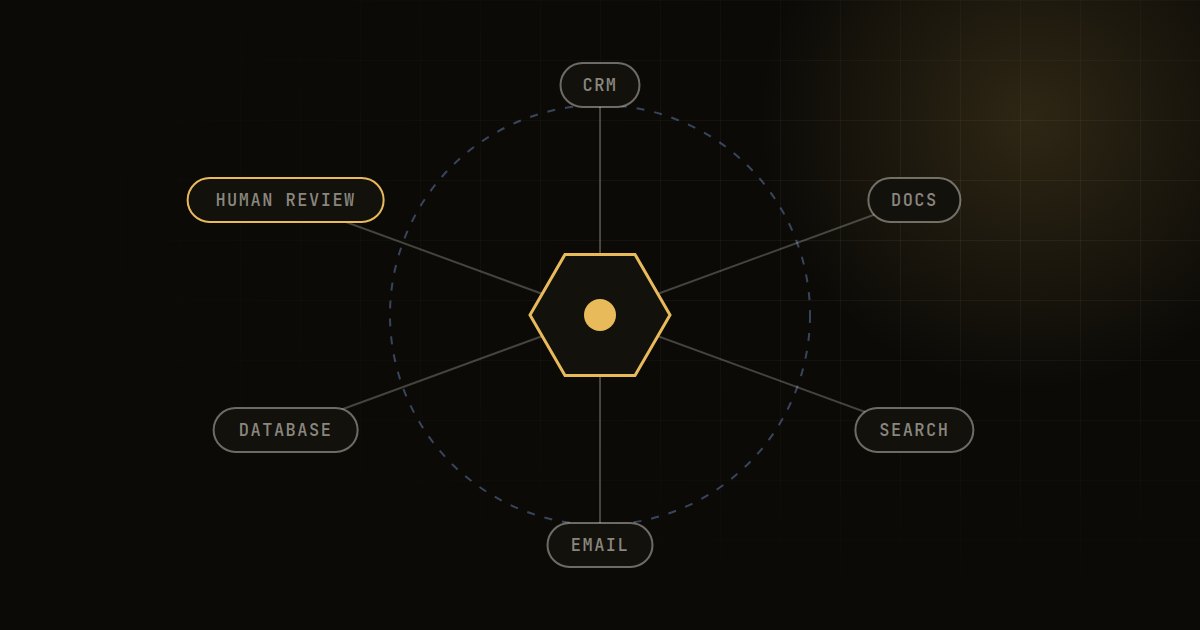
A practitioner's guide to taking enterprise AI agents from demo to production: scope, architecture, guardrails, evaluation, security and rollout.
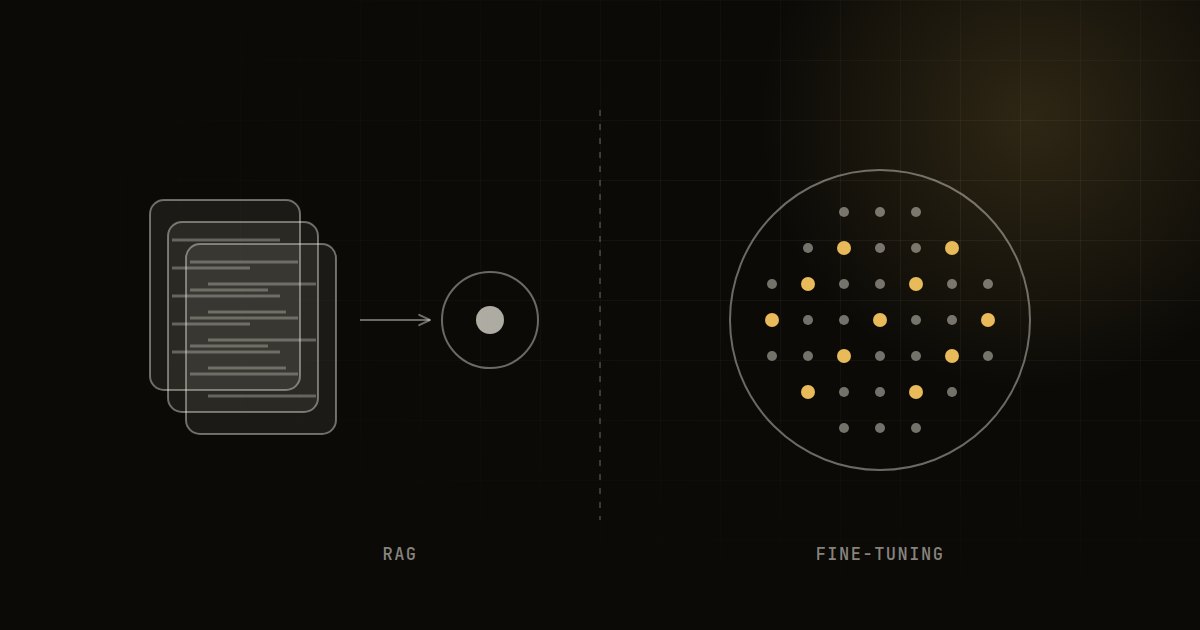
RAG gives a model the right knowledge; fine-tuning changes how it behaves. A clear comparison and decision guide for choosing between them, or using both.
Most AI pilots stall before production for predictable reasons. Here is how to spot them early and design pilots that are built to ship.